Pass leads on to other tools.
Signed, queued and retried.
Send lead events to Zapier, Make, n8n or your own system. Every delivery is signed with the webhook's own secret so the receiver can trust it, and failed deliveries are retried by the cron.
01Add a webhook
Open Setup > Outgoing webhooks (administrators) and press Add a webhook.
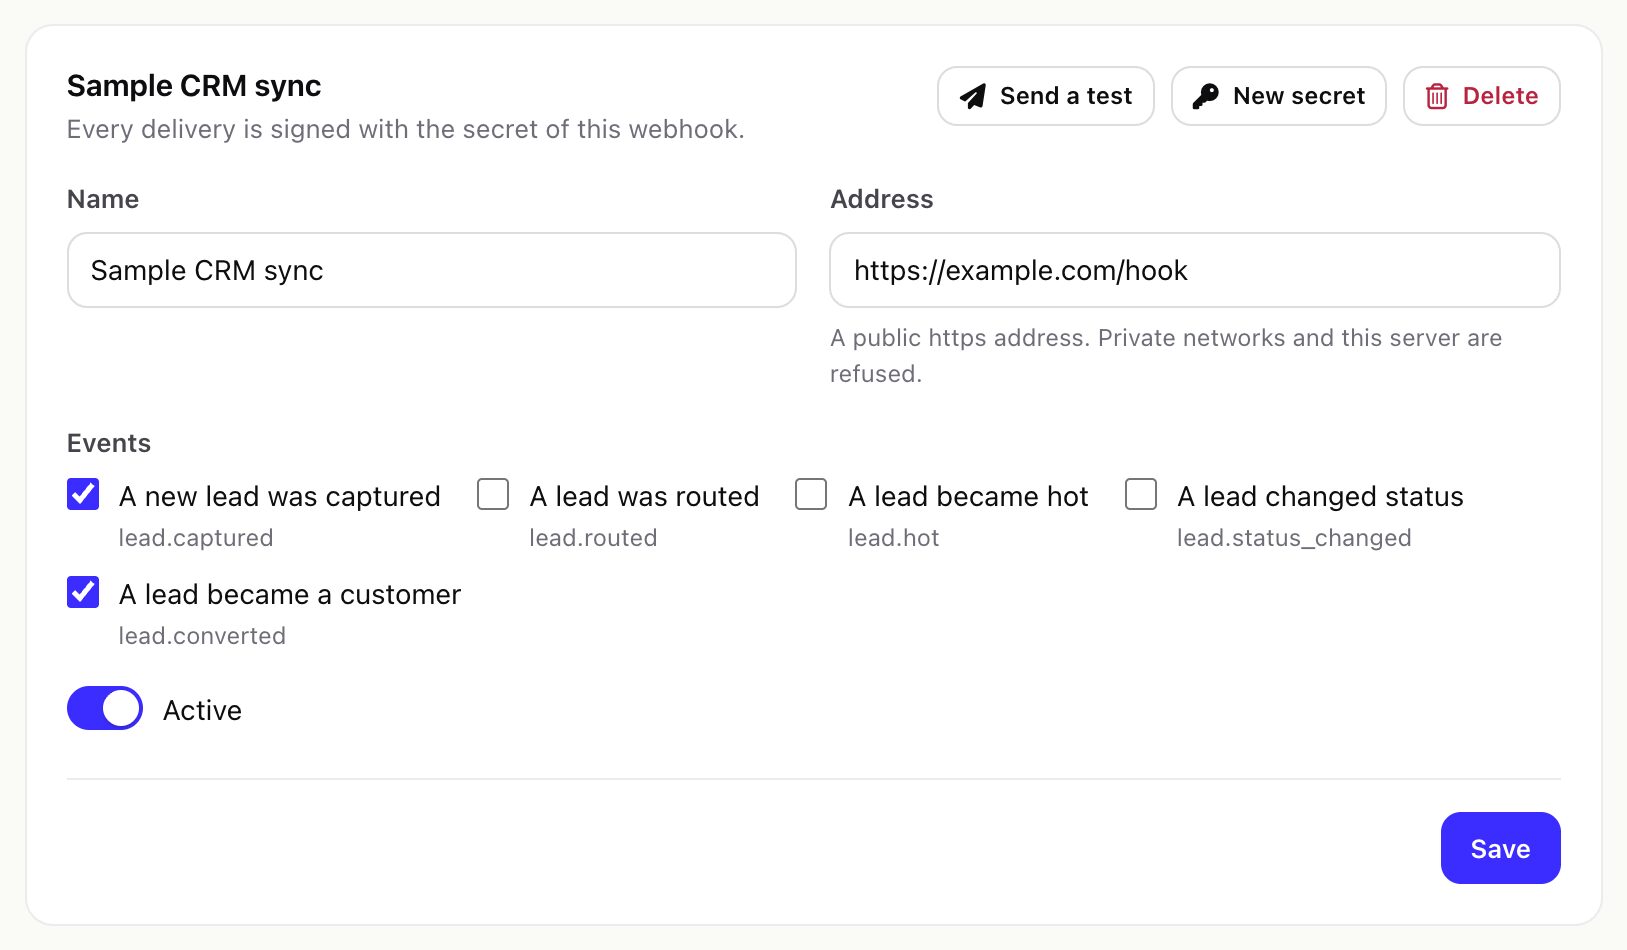
- Name and address. A public https address of the receiver. Addresses on private networks, this server or cloud metadata services are refused, on save and again before every delivery.
- Events to send (see below) and Active.
- Save and copy the signing secret. It is shown only this once. New secret makes another one; update the receiver with it.
- Send a test. Catchline sends a
pingevent and shows the receiver's HTTP answer.
02Events and their data
Every delivery is a JSON POST: {"event": "…", "created_at": "…", "data": {…}}.
| Event | When | data |
|---|---|---|
lead.captured | A submission created a new record | submission_id, connection_id, form_id, variant_id, status, target_type (lead, customer, ticket), target_id, fields (every answer), meta (page, UTM values, click ids and other source details) |
lead.routed | Routing chose an owner | lead_id, staff_id, strategy, rule_id |
lead.hot | A lead's score first reached the hot score | lead_id, score, grade |
lead.status_changed | A captured lead changed status in Perfex (seen on the cron) | lead_id, from, to (status ids) |
lead.converted | A captured lead became a customer (seen on the cron) | lead_id, client_id |
The receiver gets every answer of the form, which usually includes names, e-mail addresses and phone numbers. Send it only to services you trust and list them in your privacy notice.
03Check the signature on the receiver
Each delivery carries two headers:
X-Catchline-Event: lead.captured
X-Catchline-Signature: t=1763200000,v1=<hex>
v1 is the hex HMAC-SHA256 of the time, a dot and the raw body, keyed with the webhook's signing secret. Compute it yourself, compare in constant time, and refuse deliveries older than five minutes. In PHP:
$body   = file_get_contents('php://input');
$header = $_SERVER['HTTP_X_CATCHLINE_SIGNATURE'] ?? '';
$secret = 'YOUR-SIGNING-SECRET';
if (!preg_match('/^t=(\d+),v1=([a-f0-9]{64})$/', $header, $m)
    || abs(time() - (int) $m[1]) > 300
    || !hash_equals(hash_hmac('sha256', $m[1] . '.' . $body, $secret), $m[2])) {
    http_response_code(401);
    exit;
}
$event = json_decode($body, true);04Deliveries and retries
Events are queued and sent by the cron. Any 2xx answer counts as delivered. A failed delivery is tried again after 1, 5, 30, 120 and 720 minutes, then marked failed; the System check warns about failed deliveries. Catchline waits for the receiver up to the Outgoing timeout (Settings > Protection, default 10 seconds, 3 to 30 seconds).